OpenBSD
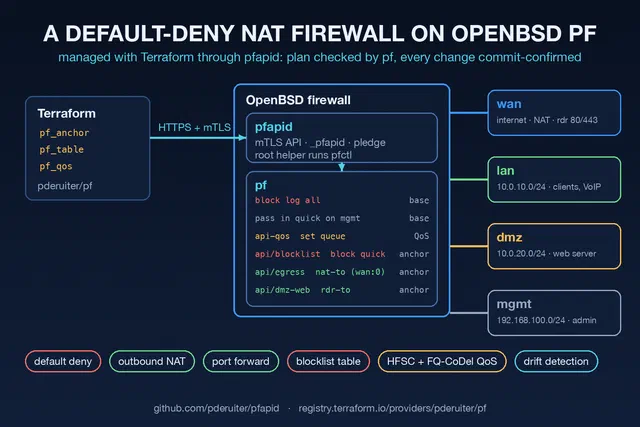
A Default-Deny NAT Firewall on OpenBSD pf, Managed with Terraform
Build a default-deny OpenBSD pf firewall with NAT, port forwarding, a blocklist and QoS, managed through pfapid and its Terraform provider.
3 articles about API.
Build a default-deny OpenBSD pf firewall with NAT, port forwarding, a blocklist and QoS, managed through pfapid and its Terraform provider.
Managing HAProxy configuration traditionally requires editing files and reloading the service.
Mutual TLS (mTLS) provides strong authentication by requiring both client and server to present certificates.