OpenBSD
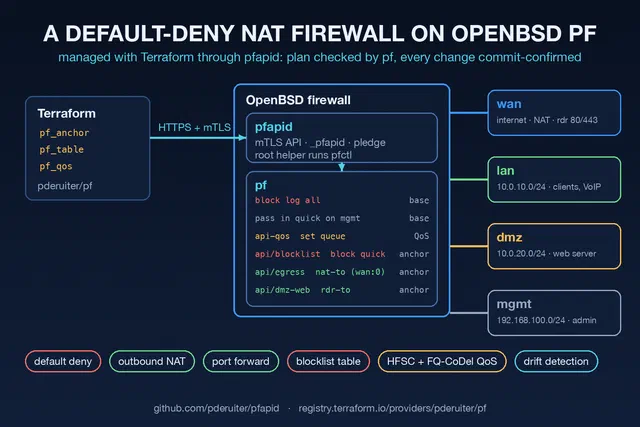
A Default-Deny NAT Firewall on OpenBSD pf, Managed with Terraform
Build a default-deny OpenBSD pf firewall with NAT, port forwarding, a blocklist and QoS, managed through pfapid and its Terraform provider.
7 articles about Networking.
Build a default-deny OpenBSD pf firewall with NAT, port forwarding, a blocklist and QoS, managed through pfapid and its Terraform provider.
DNS is critical infrastructure - when DNS fails, nothing works.
HAProxy is one of the most powerful and reliable load balancers available.
An authoritative DNS server is the definitive source of DNS records for the domains it hosts.
A recursive DNS resolver is the workhorse of DNS infrastructure, handling client queries by recursively querying authoritative nameservers until it …
Introduction OpenBSD is known for its security and clean design, making it an ideal choice for a VPN server.
TACACS+ (Terminal Access Controller Access-Control System Plus) is a protocol that provides authentication, authorization, and accounting (AAA) …