MCP
Six MCP Servers, and No Secret in Any Client
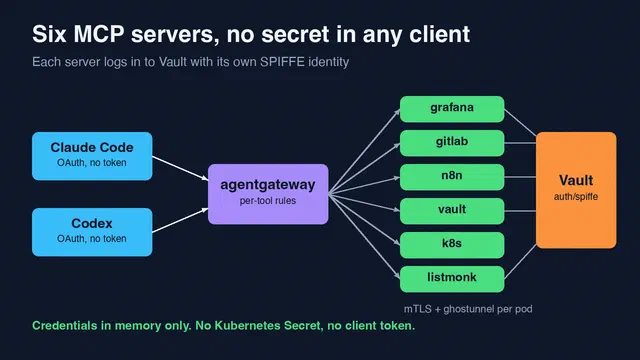
Phase 2 of our MCP platform. Six MCP servers on Talos get their credentials from Vault with their SPIFFE identity, and the AI clients keep no tokens …
5 articles about SPIFFE.
Phase 2 of our MCP platform. Six MCP servers on Talos get their credentials from Vault with their SPIFFE identity, and the AI clients keep no tokens …
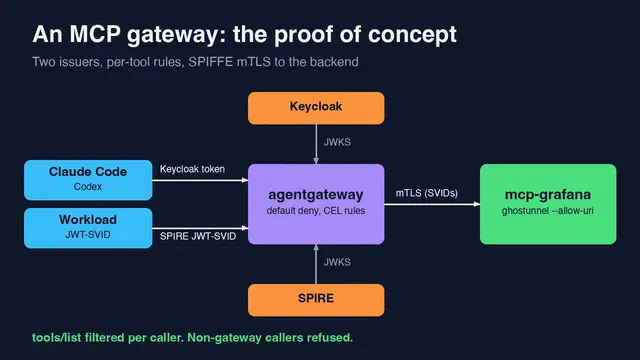
agentgateway in front of an MCP server on Talos. SPIRE JWT-SVIDs for workloads, Keycloak OAuth for people, mTLS to the backend, and one issuer …
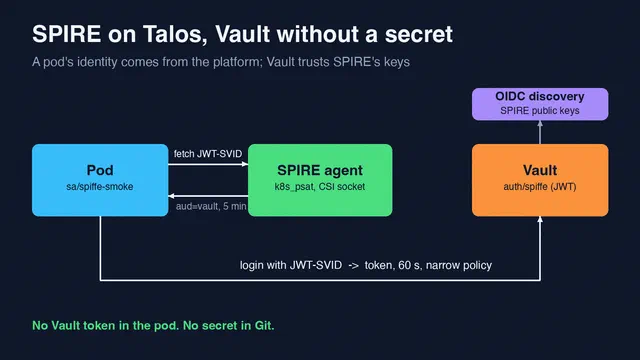
We installed SPIRE on a Talos cluster with Flux and let pods log in to Vault Community with a JWT-SVID. No Vault token, no secret in the pod.
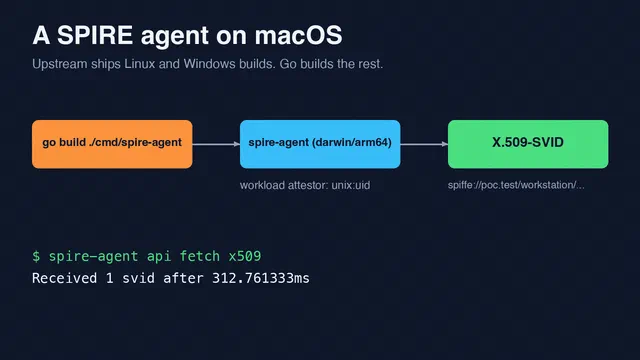
SPIRE ships no macOS build. We compiled spire-agent for Apple Silicon and got a working X.509-SVID in a local end-to-end test.
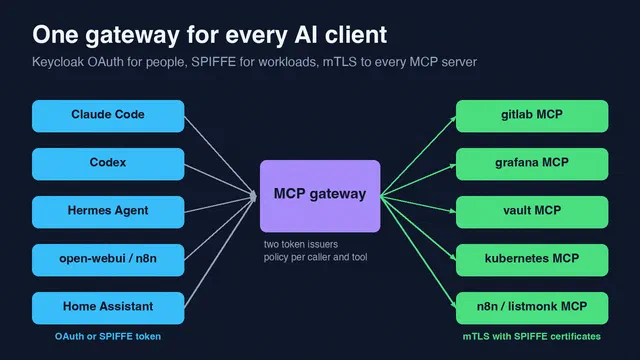
Our MCP servers move to Kubernetes behind one gateway. Keycloak OAuth for people, SPIFFE for workloads, and no public endpoint.